CVE Watch: turn an exploited-vulnerability feed into an exposure decision
A vulnerability feed is useful when it helps you decide what to check next. It is less useful when a severe number is presented without the affected product, version, exposure, or fix. CVE Watch brings vulnerability information together; your task is to establish whether a particular record applies to a system you actually operate.
In this guide
- CVE Watch: turn an exploited-vulnerability feed into an exposure decision
- CVE, CVSS, and KEV are different kinds of information
- Check applicability before prioritising a patch
- Read due dates in their actual scope
- A practical triage workflow
- Why this guide avoids an undated “worst CVE today” list
- Questions readers often ask
Start with the CVE identifier and follow the linked authoritative record or vendor advisory. A product name alone is not enough. The affected versions, vulnerable component, required conditions, and available remediation determine whether the item belongs in your own work queue.
CVE, CVSS, and KEV are different kinds of information
CVE is an identifier for a publicly described vulnerability. CVSS is a severity-scoring framework whose vector describes assumptions and impact. CISA KEV is a catalog of vulnerabilities known to have been exploited in the wild. A high CVSS score is not proof of current exploitation, and absence from KEV is not proof that a vulnerability is harmless or never exploited.
| Field | What to use it for | What to avoid inferring |
|---|---|---|
| CVE ID | Locate the specific record and advisory | That a similarly named product is affected |
| CVSS score and vector | Understand severity under the stated assumptions | The probability that your server is being attacked |
| KEV inclusion | Identify known exploitation and catalog requirements | That every machine running the product is vulnerable |
| Vendor affected-version range | Establish applicability | That a version label alone proves the vulnerable feature is enabled |
| Fixed version or mitigation | Plan a supported response | That a page refresh or a generic restart fixes the issue |
Records can be updated, disputed, rejected, or awaiting enrichment. Missing enrichment is not a zero severity. Read the record state and dates before treating incomplete fields as a conclusion.
Check applicability before prioritising a patch
For each item, answer four concrete questions: Do we run the affected product? Is the installed version affected? Is the vulnerable component or configuration present? Can the relevant attack path reach it? An internet-facing service and an unused package on an isolated machine may need different urgency even when the CVE number is the same.
Do not substitute a product guess for an inventory check. Obtain the installed version from the application or package inventory, and compare it with the vendor’s affected range. Where a distribution backports fixes, the upstream version number alone may not tell you whether the distribution package is patched; use the distribution’s security advisory as well.
KEV status is a strong reason to inspect exposure promptly. It is one input alongside asset importance, attack prerequisites, available fixes, and your organisation’s response requirements. It should not replace those checks with a blanket rule that every KEV item always outranks every other vulnerability in every environment.
Read due dates in their actual scope
CISA catalog entries can contain required actions and due dates under the relevant federal directive. Those fields are not universal legal deadlines for every website operator in the world. They are valuable context, but your own obligations depend on the applicable organisation, jurisdiction, and policy.
Preserve the advisory’s scope when sharing a record. “CISA lists a due date” is different from “every user must patch by that date.” Link the catalog entry and the vendor guidance so the reader can see both the evidence of exploitation and the supported remediation.
A practical triage workflow
- Open the CVE’s source record and vendor advisory; verify the identifier and current status.
- Match the affected product and version against an actual inventory entry.
- Check vulnerable components, configuration, and reachable attack paths.
- Read known-exploitation information and the relevant severity vector.
- Identify the supported fixed release or mitigation, and plan verification for the affected component.
- Record the action, advisory version/date, and result. A disappearing feed item is not proof that your asset was fixed.
This workflow avoids two costly extremes: treating every severe headline as an emergency on every machine, and dismissing a record merely because a score or enrichment field is missing.
Why this guide avoids an undated “worst CVE today” list
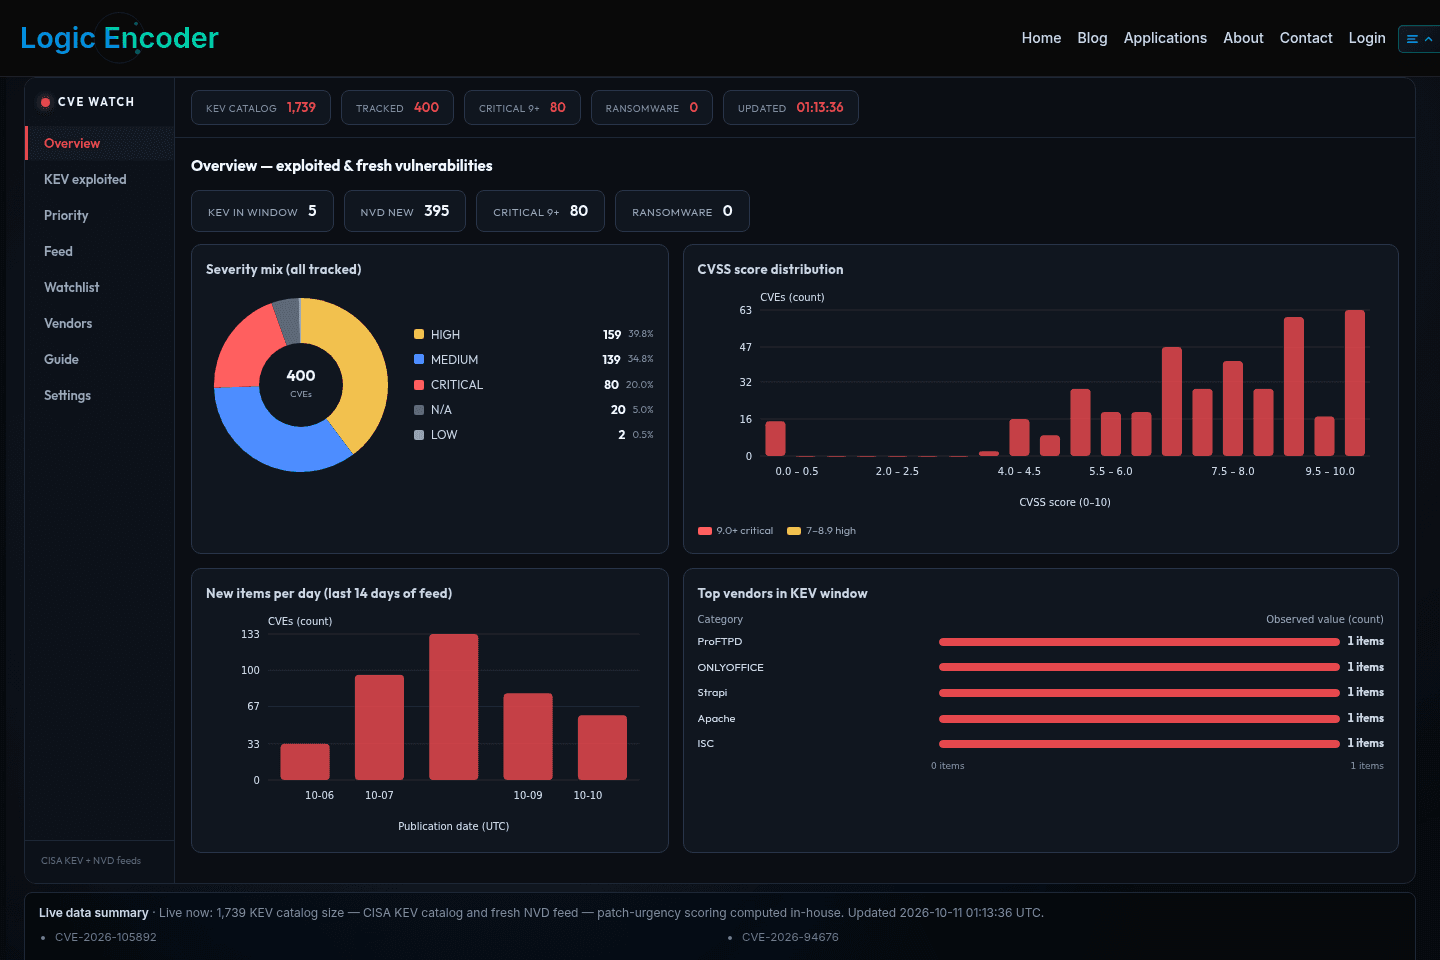
Feed counts and highlighted vulnerabilities change. A specific claim about a product, score, or exploitation needs a current authoritative record and an observation date. A fixed example without that evidence can mislead someone months later. Use the live board for current entries and the source record for the exact claim; this guide focuses on the process that remains useful after the list changes.
Questions readers often ask
Does a CVSS 10 mean my server is compromised?
No. It is a severity assessment, not a finding about your machine. Establish applicability and inspect the relevant system evidence.
Is a vulnerability safe if it is not in KEV?
No. KEV is evidence of known exploitation for listed records, not a complete list of every risk or every attack.
Why is a new CVE missing a score or detailed analysis?
The record may be awaiting enrichment or a source update. Check the vendor advisory and record state rather than treating missing data as reassuring.
Is installing an update enough to close the item?
Verify the fixed package or application version, restart or redeploy the affected component where required, and follow the vendor’s verification guidance. A queued update is not the same as an active fixed service.
Primary references: CISA’s KEV catalog, NIST’s National Vulnerability Database, and FIRST’s CVSS specifications. The board is a discovery aid; these records and vendor advisories establish the facts for a specific vulnerability.